CyberAgents Exchange Digest: November 9–13, 2026
A builder interview on Nick Solimini's CVE Impact Analyzer, submitting to the Exchange from Claude Desktop and Cowork, Exploit Dispatch and a PHP2Shell coverage check from Lance Duvall, an evidence-backed vulnerability prioritizer, a login-script builder for Tenable WAS scans, and SWARM medals on the winning listings.
November 13, 2026
🔦 Spotlight#
CVE Impact Analyzer. When a new CVE drops, the first question is whether you’re exposed, and the usual answer is to wait for plugins and then run a scan. Nick Solimini, Senior Enterprise Security Engineer at Tenable, built this skill so you don’t have to wait. Tenable already knows what software runs in your environment from your earlier credentialed scans. Give the skill a CVE ID and it finds the affected versions, checks them against that inventory, and sorts every asset into confirmed vulnerable, likely vulnerable, patched or not detected. In the interview, Nick asks about a recent OpenSSH vulnerability through the Tenable Hexa AI MCP and has the answer in seconds.
CVE Impact Analyzer Builder Interview
Get your own builder interview.Book a spot →
🎉 Celebrations#
Contributions
Five new listings this week, two of them from Lance Duvall.
- 🧩 CyberAgents Exchange Submit for Claude Desktop & Cowork by @jtbuchanan-tenb — The Desktop and Cowork edition of the Exchange submission builder. It walks you through connecting GitHub, scans the full git history for secrets before anything goes public, inventories every listable component in the repo, and opens one pull request per listing after you confirm. Its scripts are standard-library Python, so it runs in sandboxes where package registries are blocked. If you built something during SWARM Global and haven’t listed it yet, this is the easiest way in.
- 🧩 Exploit Dispatch for Tenable by @lanz — Takes the findings Tenable flags as exploited or in the news and opens one ServiceNow ticket per fix for the team that owns the assets. PagerDuty is paged only for new urgency on critical or internet-facing assets, so pointing it at an old backlog doesn’t wake anyone at 3 a.m. After rescans it closes the tickets Tenable confirms are fixed. A person approves every plan before anything is sent.
- 🧩 PHP2Shell Coverage Check by @lanz — A host with no PHP2Shell finding might be patched, or it might never have had the right scan. This skill tells them apart for every host where Tenable has seen PHP, gives each one a verdict and a reason, flags end-of-life PHP, and prints the list of hosts to rescan. Works from Tenable VM, Security Center or
.nessusfiles. - 🧩 Vuln Prioritizer by @alkaf499 — Turns a Tenable inventory into a tiered remediation worklist where every row carries its evidence, tier, SLA and due date. It scores CVSS, VPR, EPSS and CISA KEV, then adjusts for asset exposure and criticality from your CMDB. The same inputs always give the same output, so you can reconstruct a disputed deadline months later. Read-only against the tenant.
- 🤖 AuthRecon Suite by @authrecon — The hardest part of authenticated web app scanning is getting the scanner logged in. Give AuthRecon a login URL and a test account and it works out the login type, from plain forms to Azure AD, Okta and SAML, then hands back a verified Selenium
.sidescript and the exact values for a Tenable WAS scan. A self-hosted Docker stack with no cloud services.
Badges earned
Nick Solimini (@bking34) earns a Builder Interview badge for this week’s Spotlight on CVE Impact Analyzer.
Builder Interview
🛠️ Changelog#
SWARM medals on the winning listings
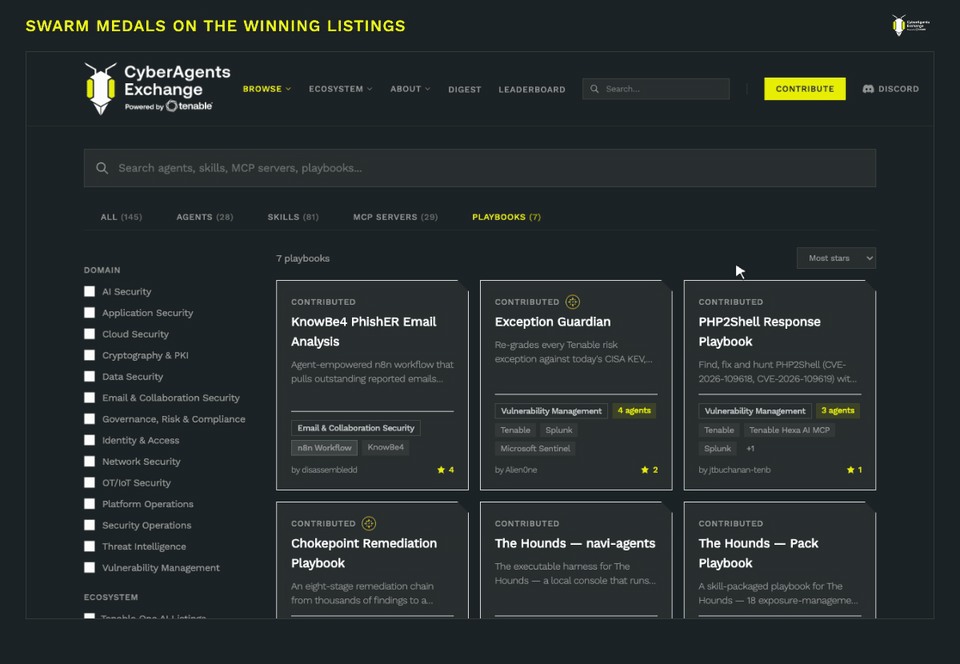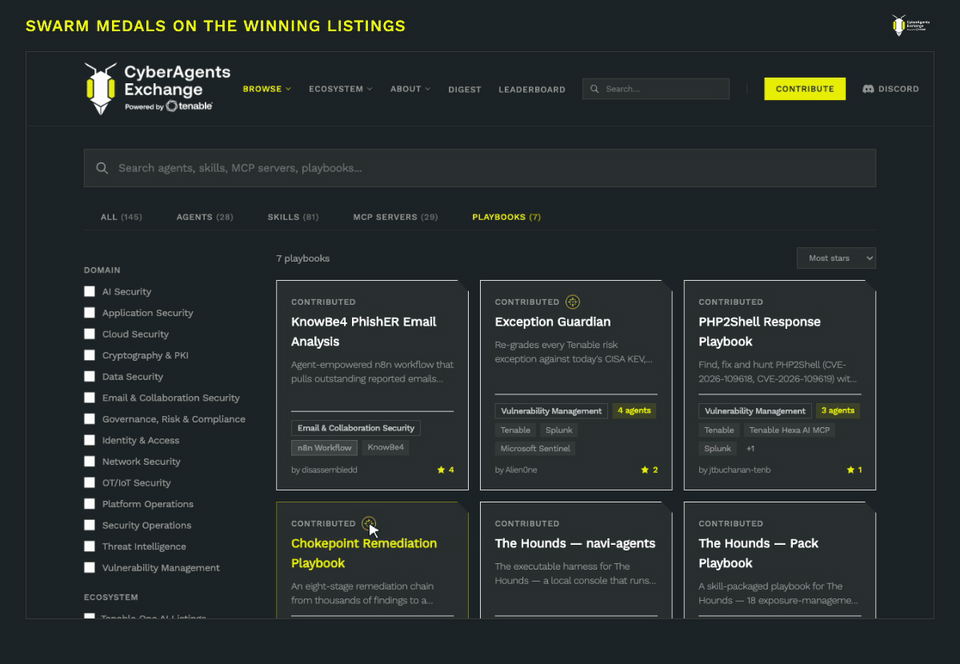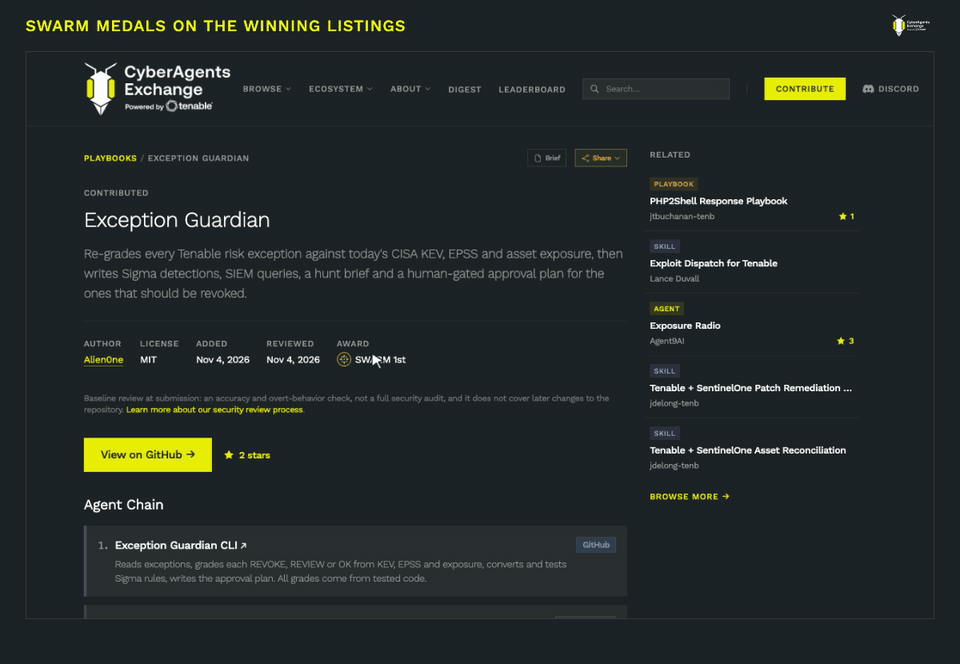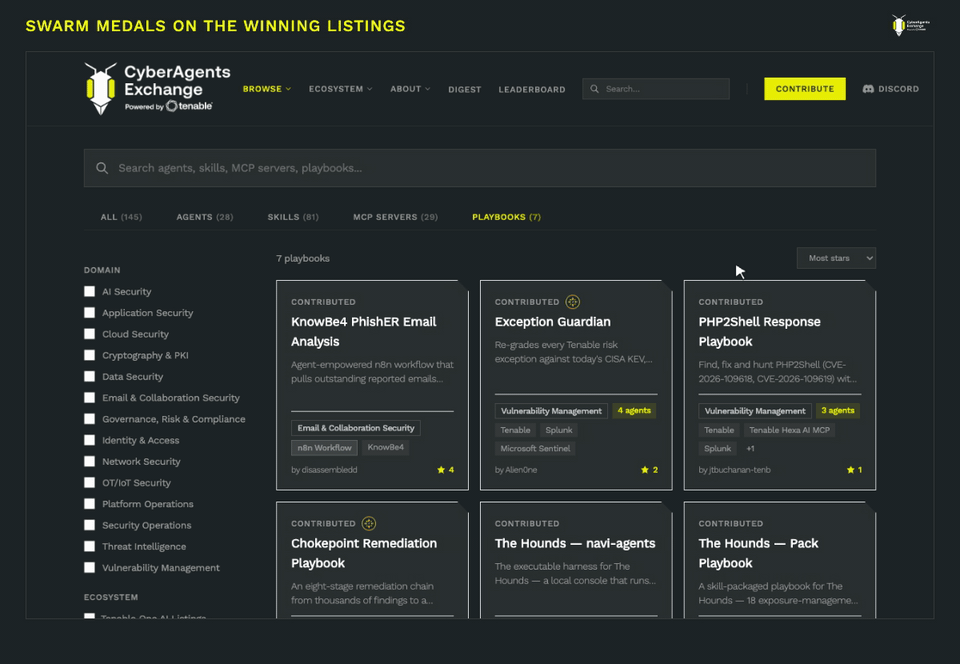
The six placed SWARM entries from Black Hat USA and SWARM Global now show their medal on the listing itself. Look for “SWARM 1st”, “2nd” or “3rd” beside the trust tier on browse, homepage and profile cards, and in the Award column on each listing’s page. Contributor badges say who placed. The medal says which of their listings won.
For agents reading the Exchange
The API manifest now gives each listing type its own detail URL pattern, so an agent looking up a skill goes straight to /api/skills/<slug>.json instead of guessing.
Tell us what you think
Is there a security job you still do by hand that an agent should take off your plate? Tell us on Discord, or email [email protected].
💬 Community#
- Welcome to George_, and thanks to Rennes and the Triple R Squad for the kind words about SWARM Global.
- Fredy Alvarez wants something basic to start with in a busy SOC. If you know the listing to try first, answer Fredy in #intros.
- Thursday’s AI in Security News included a pentest agent that escaped its sandbox. That’s a good reason to keep a person approving what your agents do.
What a SWARM winner told us. At last Friday’s Exchange Hours I talked with Narasimha (@alien0ne), whose team wh0-Kn0w5 won SWARM Global with Exception Guardian. His tip for builders is to put as much care into how you present your project as into building it. He also had ideas for making the next SWARM easier to join and get started in, and we took notes. Got your own? Tell us on Discord, and tag us on X or LinkedIn when you post about your build.
Don’t forget to say hello in #intros and tell us what you’ve built with AI lately.
📅 Events#
Exchange Hours, today at 1:00 p.m. ET
Every Friday in the General voice channel, with the next one on November 20. Bring what you’re building, or just come say hi.
Until next time,
— Bee
Join the community
Build the future of security, together.
Trade notes with peers on agents, skills, MCPs, and playbooks instead of building in isolation, swap tips and tricks, build in public, and catch events and community calls.
Join the community