CyberAgents Exchange Digest: November 2–6, 2026
The SWARM Global winners, thirteen new listings from a risk-exception re-grader to a security radio station, and a new homepage.
November 6, 2026
🔦 Spotlight#
The SWARM Global winners. Teams spent November 2 to 6 building security agents for SWARM Global, then pitched them to judges from Tenable and Anthropic. Here’s who came out on top.
- 🥇 Exception Guardian by wh0-Kn0w5 (@alien0ne) — Re-grades every Tenable risk exception against today’s threat data, then writes the detections and the approval plan for the ones that should be revoked.
- 🥈 Tabletop GM by gcd (@eshin087) — Runs an incident response tabletop built from your own exposure data and scores it the same day.
- 🥉 RBVM Agent by Triple R (@sadybeca) — Groups Tenable findings into cards for the team that owns the fix and keeps Azure DevOps in step.
Honorable mentions go to Astelia for Porygon Mitigator, which plans mitigations for the findings an attacker can reach through your firewalls, and to agent9.dev for Exposure Radio, a security radio station for small IT teams.
Thank you to every team that built something, and to the judges who heard them out. You’ll find all five, and more from the week, under Contributions.
🎉 Celebrations#
Contributions
Twelve of this week’s thirteen new listings came out of SWARM Global. The other one is Tenable Report Workshop.
- 📋 Exception Guardian by @alien0ne — Re-grades every Tenable risk exception against today’s CISA KEV, EPSS and asset exposure. For each one that should be revoked, it writes Sigma detections, Splunk and Sentinel queries, a hunt brief and an approval plan that a person signs off on.
- 🧩 Tabletop GM by @eshin087 — Runs an incident response tabletop built from your own exposure data. Put Claude Code on the projector and Claude presents each inject, plays the CEO, the regulator and the press when the room stalls, and logs every decision. Type END and the room gets a scored after-action report. Injects quote your own IR plan word for word, and ten industry packs carry real notification deadlines with sources.
- 🤖 RBVM Agent by @sadybeca — Team Triple R’s SWARM entry, from Rennier Mazuco, Rafael Codeceira and Rebeca Ribeiro. It pulls findings from your own queries through Hexa AI in Tenable VM, groups the ones that share a fix and an owning team into one card, and opens and closes Azure DevOps work items to match.
- 🤖 Porygon Mitigator by @ori-astsec — For the findings you can’t patch tonight. It works out which Tenable findings an attacker can actually reach through your firewalls, finds mitigations that stop them without breaking allowed traffic, and writes the exact change for a person to approve.
- 🤖 Exposure Radio by @agent9ai — A security radio station for small IT teams that never get a standup. Two hosts compare yesterday’s and today’s Tenable VM exports and brief what’s new, what to fix first and what was verified fixed, between weather, CISA news and music. Every exposure line is rebuilt from typed evidence and has to pass a claim check before it airs.
- 📋 Email-Analyst-in-a-box by @austinsr1 — Campus Autonomous Defenders’ SWARM entry. An eight-stage local triage chain for user-reported phishing that takes on the part of an analyst’s day spent proving a message was nothing. It stops at a human checkpoint before any change outside the box.
- 🤖 ThreatWeave AI by @sreedhar51 — Links Tenable vulnerabilities to failed CIS checks on the same asset and to human-verified CMDB context, then ranks candidate fixes with a deterministic policy engine. Every run writes a Decision Receipt, so you can replay two runs and see exactly why a ranking moved. Read-only.
- 🔌 RiskProof by @creimer808 — Investigates Tenable and Nessus findings instead of rescoring them. It adds EPSS, CISA KEV and optional GreyNoise signals, checks scanner claims against observed versions to flag likely false positives, and runs non-destructive checks only against targets on your allowlist.
- 🔌 Exposure Case Builder by @spookyfox9 — Turns a saved Tenable VM export into ranked cases for the security team and fix packages for engineers. Exploited single vulnerabilities and patch backlogs come back as separate lists, so a big OS backlog can’t bury a KEV finding. Claude writes the cited narrative and the analyst records the decision.
- 🔌 ScreenWarden by @the-cyberlayer — Android phone tools for AI agents, with guardrails built in. It strips text a person can’t see from every screen and checks each action before adb runs it, so a fake bank SMS can’t talk the agent into forwarding your login code.
- 🧩 SecOps Autopilot by @sword0x00 — Carries a CVE from detection to a verified fix. It finds the affected assets in Tenable, scores them against a KRI register, plans patches and compensating controls, and opens a ticket only after a recorded human approval. It finishes with an audit-ready evidence package.
- 🤖 Tenable Report Workshop by @blckdvc — A local web app and CLI that turns Security Center or Tenable VM data into branded PDF and Excel remediation reports. It folds a pile of “Product < X” findings into one “install version X or later” action. Runs on 127.0.0.1 with no telemetry.
- 🔌 maskline by @engineeringergonomics — Checks agent transcripts and build logs for leaked secrets before you share them, shell-trace lines like
+ export KEY=...included. You get the findings by line and a redacted copy. Standard-library Python with no network access.
Badges earned
🛠️ Changelog#
A new homepage
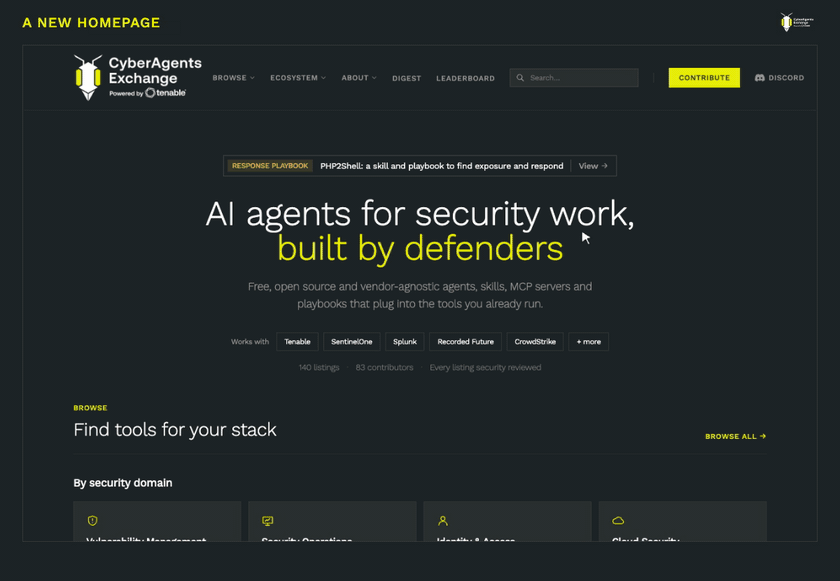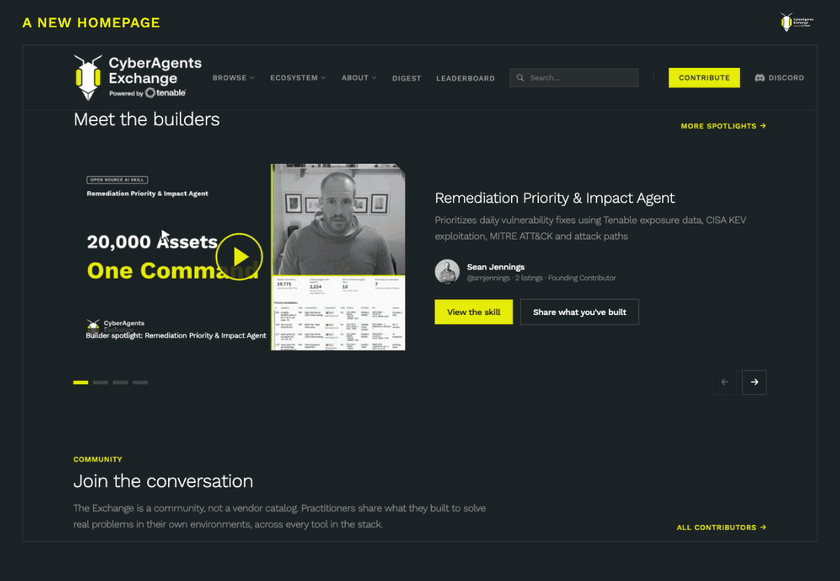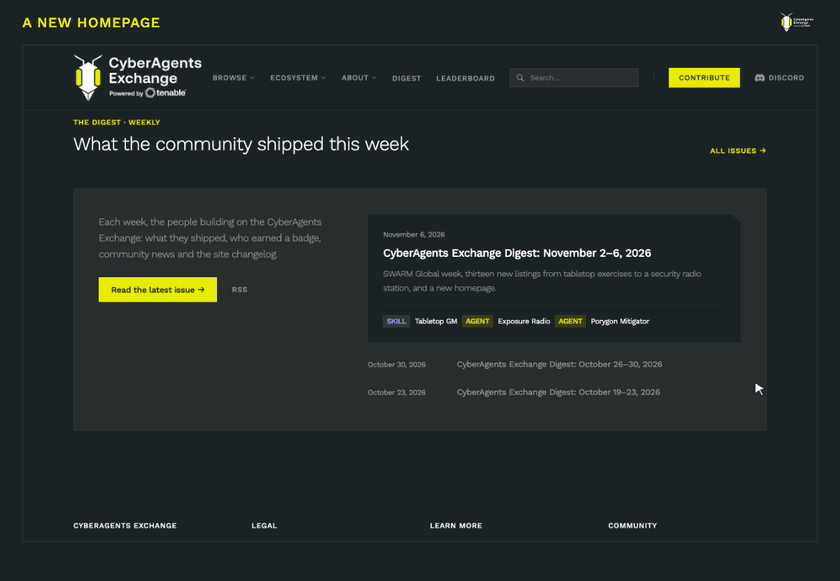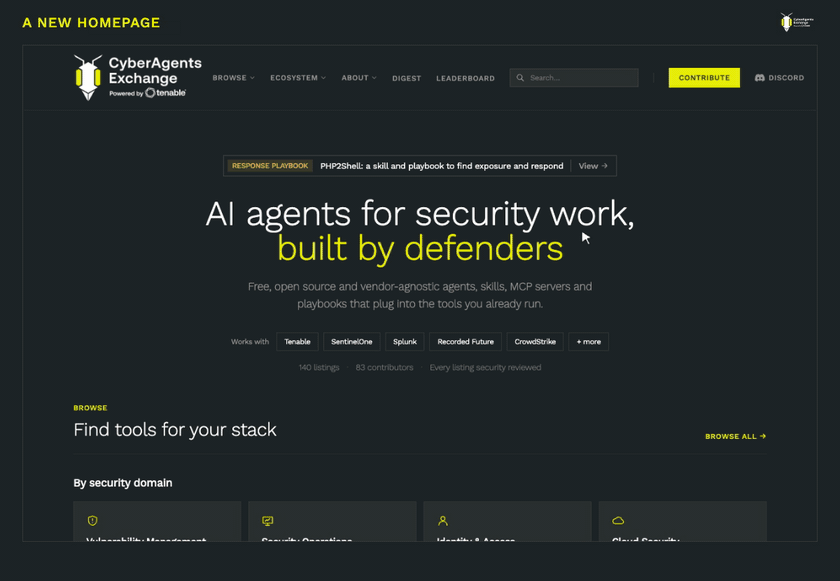
The homepage now starts with what you came for. Browse by security domain from a grid of tiles, or jump straight to agents, skills, MCP servers or playbooks. Below that, the builder spotlight is a carousel with one builder interview for each listing type, then our Contributing Partners, a way into the Discord and Exchange Hours, and the latest three Digest issues.
Tell us what you think
Thirteen new listings in one week is a lot of new ideas, and we want yours too. What should the Exchange do next? Come tell us on Discord, or email [email protected].
💬 Community#
SWARM Global took over the Discord from November 2 to 6. Teams registered on Monday, built through Wednesday and pitched to judges from Tenable and Anthropic on Thursday. Friday’s awards ceremony named the winners, who lead this issue’s Spotlight.
How the week went
- Monday’s kickoff laid out the schedule, and team registration closed that night.
- Tuesday brought an optional session on best practices for building AI agents.
- PRs to the CyberAgents Exchange were due Wednesday at 2 p.m. ET. Selected teams heard back that afternoon and pitched on Thursday.
- The top three teams split $10,000 in Claude credits.
#swarm-help was busy
Builders asked for Tenable One lab tenants with synthetic data, and the team set them up as the requests came in. The question we heard most was whether a build needs the Hexa AI MCP or Tenable data. It doesn’t. Any agent, skill, MCP server or playbook qualifies, as long as it handles a real security workflow.
Built in public
agent9.dev shared their open-source project that turns Tenable scans into a morning radio show. You’ll find it on the Exchange as Exposure Radio.
New faces
Fifty people joined during SWARM week, bringing the server to 267 members. Twenty-two of them arrived on kickoff day. People said hello in #intros from Nashville, Dallas, Indiana, San Jose and Juárez, Mexico, and one SWARM team is building from Brazil.
Don’t forget to say hello in #intros and tell us what you’ve built with AI lately.
📅 Events#
Exchange Hours, Friday, November 6 at 1:00 p.m. ET
Every Friday in a Discord voice channel. Bring what you built for SWARM.
The attacker-defender race: Building frontier-ready cybersecurity agents, Tuesday, November 10 at 11:30 a.m. ET
Sean Jennings of Tenable and Brett Andrews of Anthropic on what 500+ hours of testing Claude Mythos Preview revealed, and how Adversary View in Tenable One finds vulnerability chains and the fix that breaks each one.
Until next time,
— Bee
Join the community
Build the future of security, together.
Trade notes with peers on agents, skills, MCPs, and playbooks instead of building in isolation, swap tips and tricks, build in public, and catch events and community calls.
Join the community